Cloud Application Development on AWS
We build cloud-native applications that live on AWS, provisioned entirely through Terraform. An environment rebuilds itself from code, without a support ticket, and a new region or account starts from the same tested foundation every time.
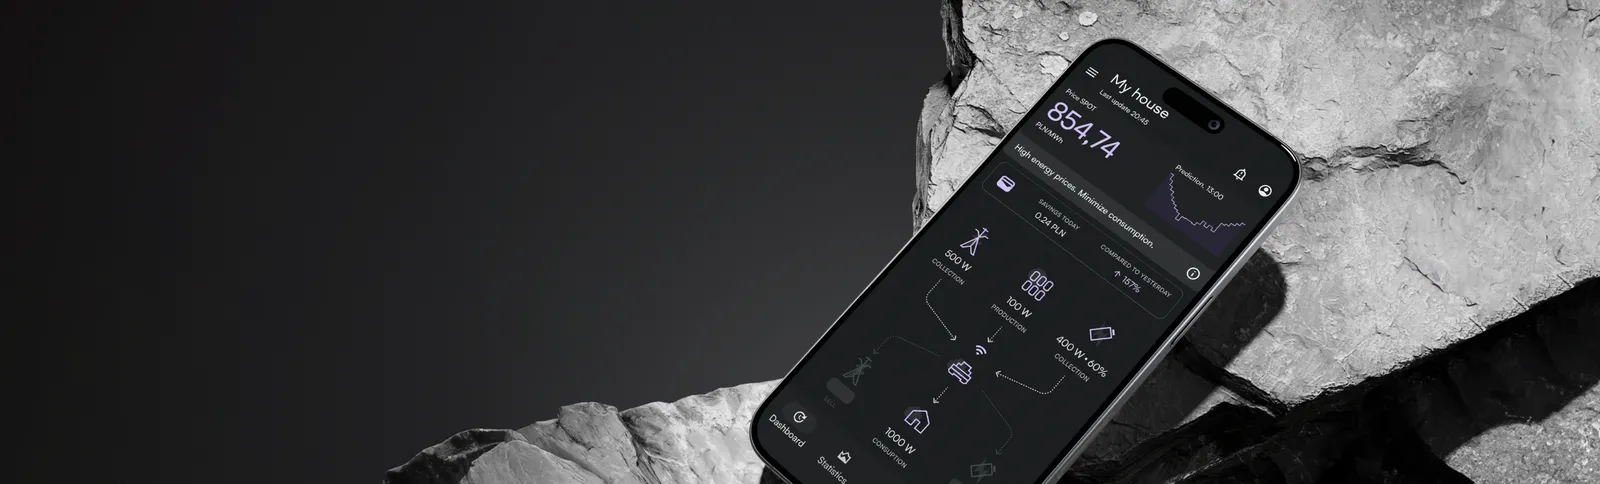
Cloud Native Application Development, Built the Same Way Every Time
Real production AWS work, end to end.
What We've Actually Built on AWS
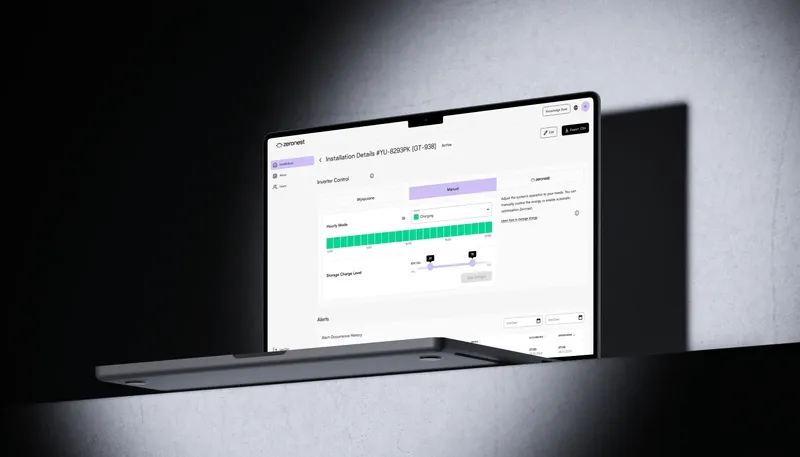
Zeronest's Energy Platform Runs on AWS
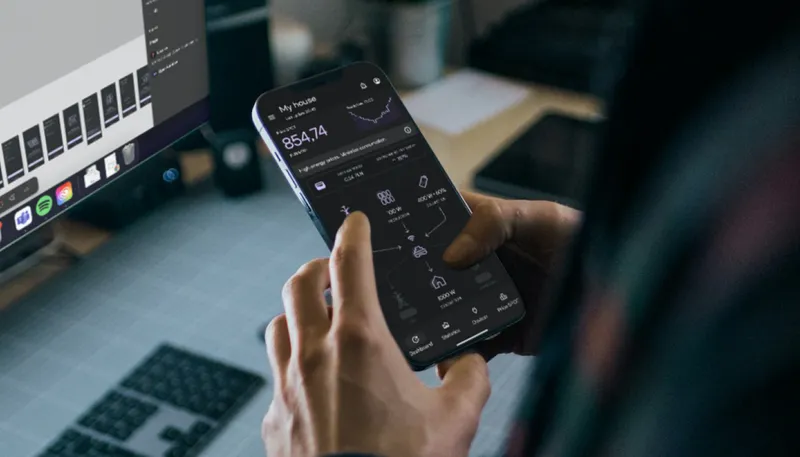
Zeronest's solar and battery management platform has been running on AWS since January 2024, now more than two years in production. The containers run on ECS, with RDS and S3 holding the data behind them. Event-driven work goes through Lambda, while Cognito manages user identity, authentication and password resets, so nobody on the team keeps a spreadsheet of credentials. Messaging between services runs through SNS, and every change to that stack deploys through GitHub Actions. Behind it, Python and Django REST Framework run the API, with Celery handling scheduled and background jobs. Terraform provisions all of it, so the setup can be audited and rebuilt from code at any time. The platform now serves several thousand users through three connected applications and covers 16 integrated inverter brands. It runs behind AWS IoT Core, with device traffic encrypted over MQTT and TLS 1.2.
One Repeatable Pattern, Applied to Every Other Account
Centrum Komunikacji (public sector communications), Ticket Club (e-commerce ticketing), and a third platform built for an industrial IoT client under NDA all run on this same Terraform-plus-AWS setup across three different industries. Each environment is defined in code, so a reviewer can read the change before it ships. Every change to the infrastructure carries an author and a timestamp, with the reason attached to the same commit. Terraform state is stored and locked centrally, so two engineers changing the same environment at once get a merge conflict rather than two AWS accounts drifting apart unnoticed. The review step, state lock and audit trail are the same in every client's account, and anyone on the team can open the Terraform files and see exactly what is running.
Working Toward AWS Partner Validation
We are working toward AWS Partner Central's Validated tier, which reviews the Terraform-and-AWS pattern already running in production for the clients above against AWS's own bar for security posture, cost management and operational practice. The review covers infrastructure defined in Terraform, environments that can be rebuilt from code, and a team that has already run this pattern across four production AWS accounts, starting with Zeronest's first environment in January 2024. The validation is currently in progress.
Why Build Your Cloud Application With Us
Infrastructure as Code, Not Console Clicks
One Cloud, Deep Expertise
Teams That Stay on the Project
Cloud Application Development on AWS, Answered
Get an estimate for the costs, timeline & the team composition needed for your project...
-
Our hands-on, repeated production experience is AWS: Zeronest, Centrum Komunikacji, Ticket Club and one more platform under NDA all run there today. We can design cloud-agnostic architectures when a client's constraints call for a different provider, but we do not claim the same production depth on other clouds, and we would say so upfront.
-
Yes, and it starts with an audit rather than a rewrite. We map what exists, stabilize what is fragile, then propose changes in that order, the same approach we followed when we took over ongoing AWS work for an existing energy-sector platform.
-
We are working toward the Validated tier of AWS Partner Central. It is a status we are pursuing and have not reached yet.
-
Autoscaling tuned to actual load rather than a fixed instance size, plus alerting that flags a cost spike while it is still small. That is the same pair of changes we added to Zeronest's RDS setup: autoscaling first, then alerts that catch what autoscaling alone would miss.
Let's Discover What Your AWS Platform Actually Needs
Your message goes to
Filip Szamborski
Board Member

Your message goes to
Karol Oponowicz
Board Member
Your message goes to
Paweł Zieliński
Board Member
SO FAR WE HAVE WORKED WITH BRANDS LIKE:

Thank you for your message.
We read every message ourselves and get back to you within 48 hrs on business days.
Something urgent? [email protected]